Enforcing password history during password reset
In a world reeling under a large number of applications to make our life easier, it is a daunting task to remember the usernames and passwords for each and every application being used. Though administrators force users to change the passwords periodically, users always tend to find a loophole to ease their task. One such trick is using the old password again while resetting the password. This is not a good idea as it sounds. Intruders must just have to try a few old passwords if they happen to be a well-known person.
ADSelfService Plus, with its highly flexible password policy enforcer, helps to implement stringent password policies. It provides an option to prevent users from using the previous 'n' number of passwords. The 'n' has to be configured by the administrators.
Steps to enforce password history
Log in to the admin portal of ADSelfService Plus.
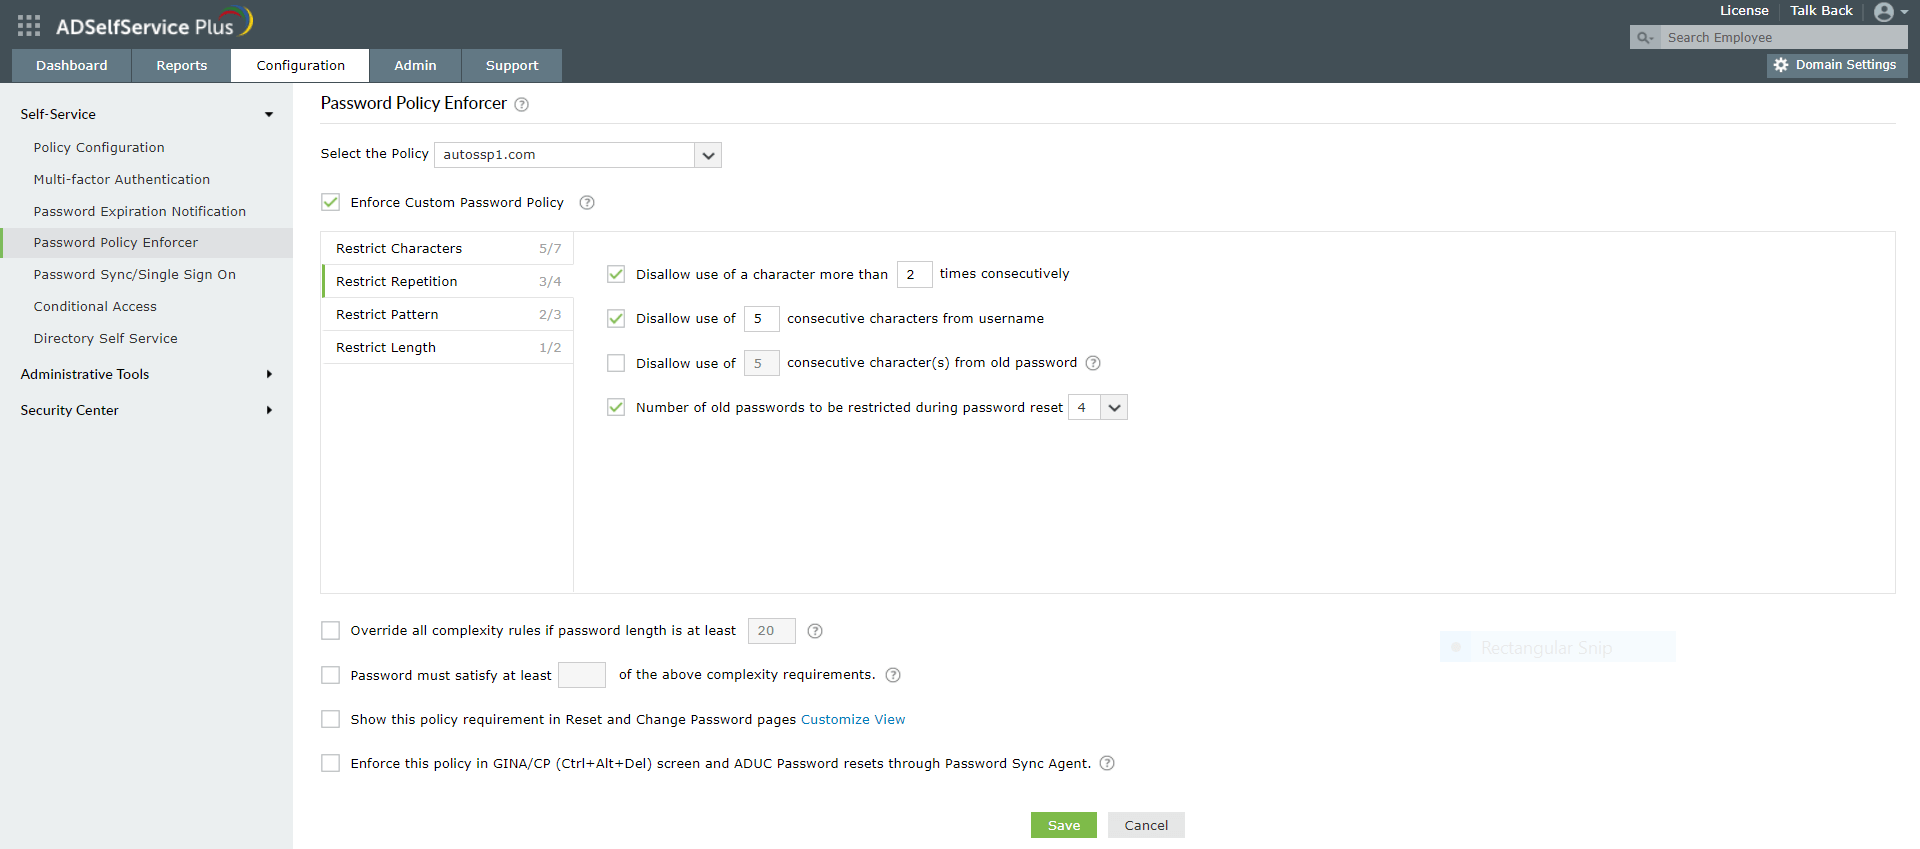
Go to Configuration > Self-Service > Password Policy Enforcer.
In the Select the Policy drop-down, select the policy for which password history must be enforced.
Enable the Enforce Custom Password Policy checkbox.
In the Restrict Repetition section, check the Number of old passwords to be remembered during password reset, and use the drop-down to select the number of passwords that must be remembered.
For example, if you select 5, users won't be able to use the previous 5 old passwords while resetting it.
Click Save.