Windows crashes caused by Crowdstrike: Workarounds
Dear customers,
We are aware that many of you are encountering issues with your Windows systems due to a problem with CrowdStrike’s Falcon Sensor. This is causing unexpected system behaviour, including blue screens and restarts.
We want to assure you that this issue is not related to ManageEngine. While we wait for a permanent fix from CrowdStrike, we are doing our best to help our affected customers with a temporary workaround.
What is the issue?
A recent CrowdStrike update of July 19, 2024 ended up having a conflict with Windows systems. It is due to a critical error caused by CrowdStrike’s Falcon Sensor that abruptly stops the machine and throws an error message on a blue screen.
Mac and Linux-based hosts are unaffected.
How do I know I am impacted?
You're likely affected if you're experiencing:
Systems are stuck at a bluescreen or a bugcheck screen .
System crashes unexpectedly or restarts frequently.
Difficulty booting your computer
What is the cause?
Crowdstrike claims this issue to be due to a single faulty channel file found in a content update for Windows hosts.
They have now reverted the changes in their latest version channel file "C-00000291*.sys".
As a temporary measure, please follow the below workarounds:
Workaround given by CrowdStrike:
- Boot Windows into Safe Mode or the Windows Recovery Environment
- Navigate to the C:\Windows\System32\drivers\CrowdStrike directory
- Locate the file matching “C-00000291*.sys”, and delete it.
- Boot the host normally.
The challenge: If a device's BitLocker is enabled, you need a BitLocker Recovery Key to enter safe mode. It can be retrieved only if it is locally stored already. Without this key, implementing the CrowdStrike workaround becomes impossible.
How Endpoint Central helps here:
Endpoint Central allows you to retrieve the key directly from the console, after which you can follow the CrowdStrike workaround.
1. Login to Endpoint Central console.
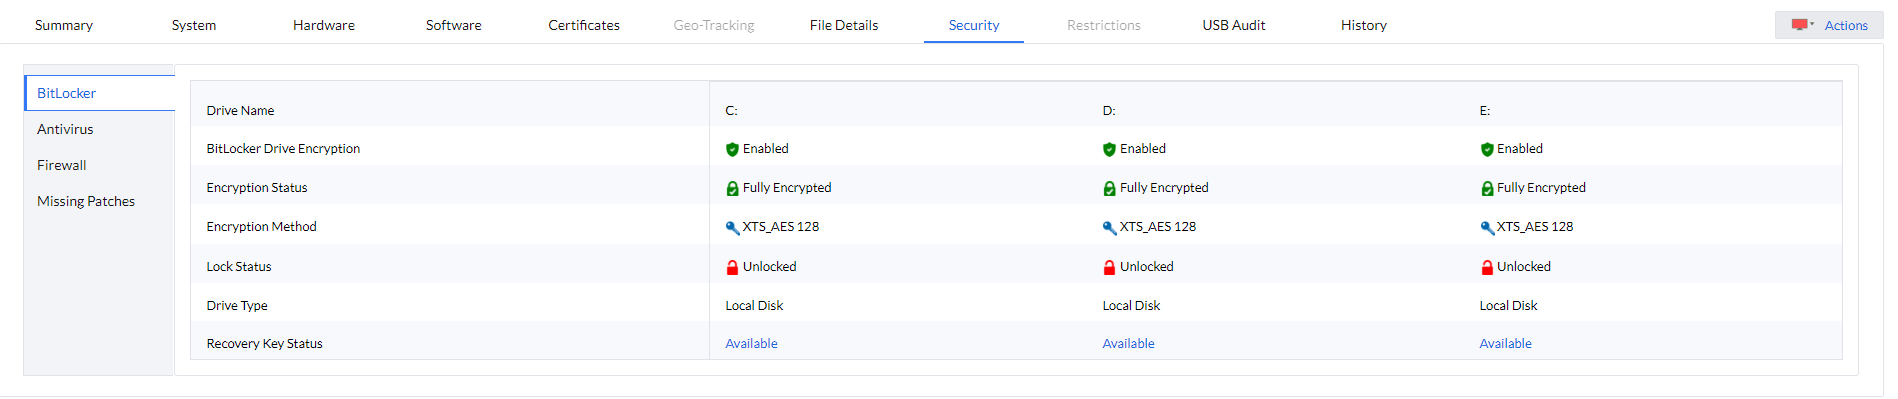
2. Go to Inventory > Computers > Select required machine > Security Tab > BitLocker.
3. Click "Available" under C Drive in the 'Recovery Key Status' tab to get the Recovery Key.
4. Boot Windows into Safe Mode or the Windows Recovery Environment. (Use BitLocker Recovery Key when asked)
5. Navigate to the C:\Windows\System32\drivers\CrowdStrike directory
6. Locate the file matching “C-00000291*.sys”, and delete it.
7. Boot the host normally.
We have built a dedicated tool that will automatically apply the CrowdStrike workaround to your machine and restart it. Visit this link for knowing more: https://www.manageengine.com/products/desktop-central/crowdstrike-windows-bsod-resolution.html
Sticky Posts
Device alerts and timeline just got smarter: Meet Alert Correlation and Zia-powered timeline insights
Hello everyone, Two important updates just landed in Endpoint Central's DEX module and both help IT teams get to root causes faster. Now, IT teams will have fewer alerts to sift through, and less time spent piecing together what actually happened on aNew feature release: Device Timeline – Visualize, trace, and troubleshoot issues faster
Hello everyone, We're excited to introduce Device Timeline, a major upgrade to Endpoint Central’s DEX module that gives IT teams a clearer, more intuitive way to investigate performance issues.This is currently available for cloud users only. This featureEndpoint Central delivered 442% ROI according to Forrester Total Economic Impact study
We are excited to share that we recently commissioned a Forrester Total Economic Impact™ (TEI) study to evaluate the potential benefits that organizations can achieve using Endpoint Central. The study found that interviewed organizations using EndpointDesktop Central protects from Win32/Conficker worm
Hi All, Today is April 1st and there is a peril of Win32/Conficker worm. Win32/Conficker is a worm that infects other computers across a network by exploiting a vulnerability in the Windows Server service (SVCHOST.EXE). If the vulnerability is successfully exploited, it could allow remote code execution when file sharing is enabled. Depending on the specific variant, it may also spread via removable drives and by exploiting weak passwords. It disables several important system services and securityManageEngine Desktop Central Supports the Greening of IT
ManageEngine Desktop Central Upgrade Supports the "Greening" of IT; Software Minimizes Energy Use Automates Shutdown of Computers During Non-Office Hours; Generates Monthly Reports Used in Claiming Utility Rebates AUSTIN, TX--(Marketwire - January 27, 2009) - ManageEngine, makers of a globally renowned suite of cost effective network, systems and security management software solutions, today announced an update to Desktop Central, the company's web-based Windows Desktop Management Software, with
Topic Participants
Reeni B
jillianmontague9
Karthikk B
sunnyveum39
Karthick CP