Protect your Office 365 tenant from risky sign-ins
A risky sign-in is a login activity performed using a user account by someone who is not the owner of that account. More often than not, it is a tell-tale indication of a compromised user account, and could pose a serious threat to the security and confidentiality of your Office 365 tenant. If the user accounts from which risky sign-ins occur are not monitored, your organization could end up losing business critical data to intruders. An important information that can help establish the legitimacy of login is location from which it occurred.
Azure Active Directory displays details about risky sign-ins to your Office 365 tenant under the Security section, Risky Sign-ins tab.
How to do it with O365 Manager Plus?
O365 Manager Plus goes one step further in monitoring risky sign-ins by offering geolocation and Client IP filtering option for audit reports and alert triggers. For actions such as login, password change and more, this option allows you to find the country from which the operation was performed, based on the IP address of the device. By combining these with the Business Hours settings, you can scrutinize the logon activity further, by checking if the sign-in happened during the designated time or not.
To create a new alert profile (to monitor logins made from outside the organization's default location or country as configured), follow the steps given below:
1. Go to the Alerts tab.
2. Click on the New Alert Profile option on the bottom left corner.
3. Select the Add Profile option.
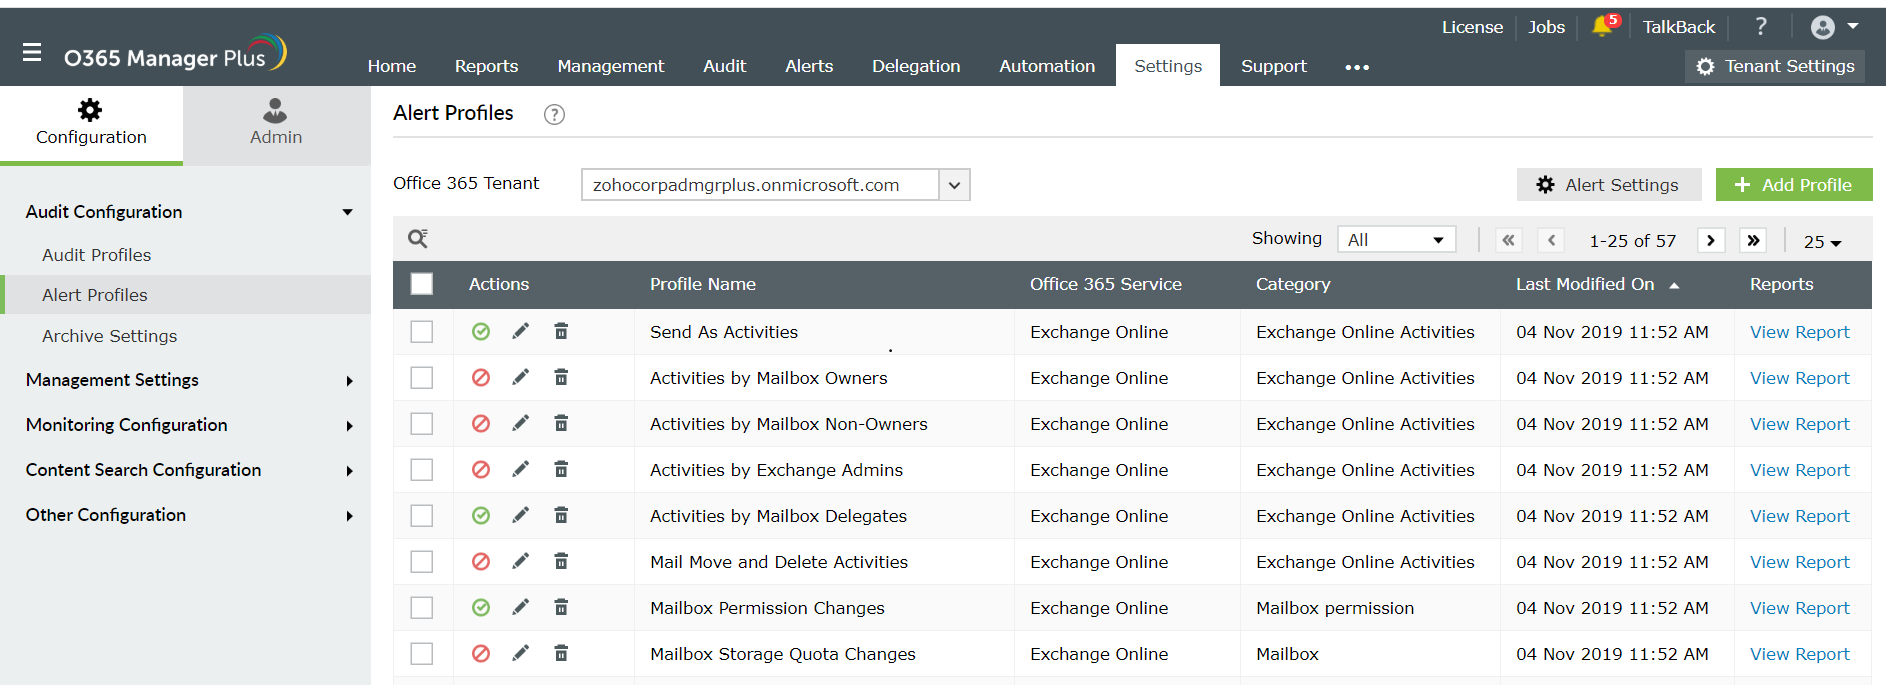
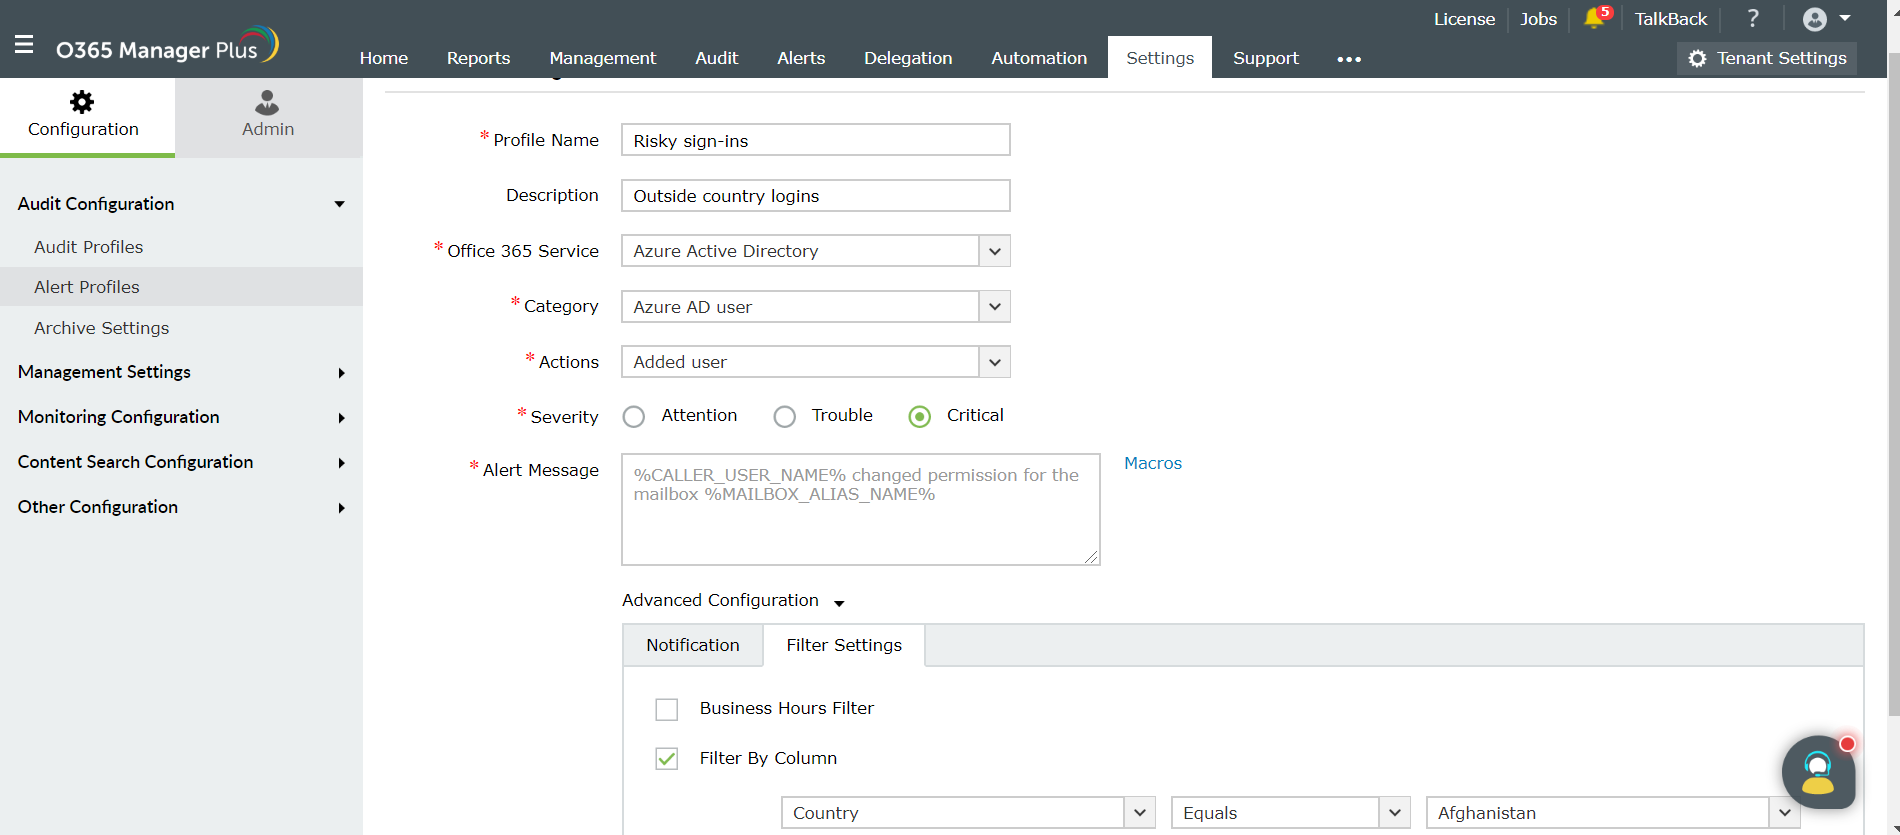
4. In the Alert Profile Configuration window that appears, enter a suitable Profile Name and Description.
5. Select the Office 365 Service as Azure Active Directory, Category as Azure AD User and Actions required.
6. You may change the level of severity and Alert Message as you prefer.
7. Under Advanced Configuration, go to Filter Settings, select Filter By Column and configure the countries for which you would like to trigger an alert.
8. Click on Add.
You can also use the Client IP filter to generate alerts as you desire. By filtering Client IPs, you can find out the activities done outside the organization network or your trusted IP ranges. You may choose to block or trust IPs based on the data you get.
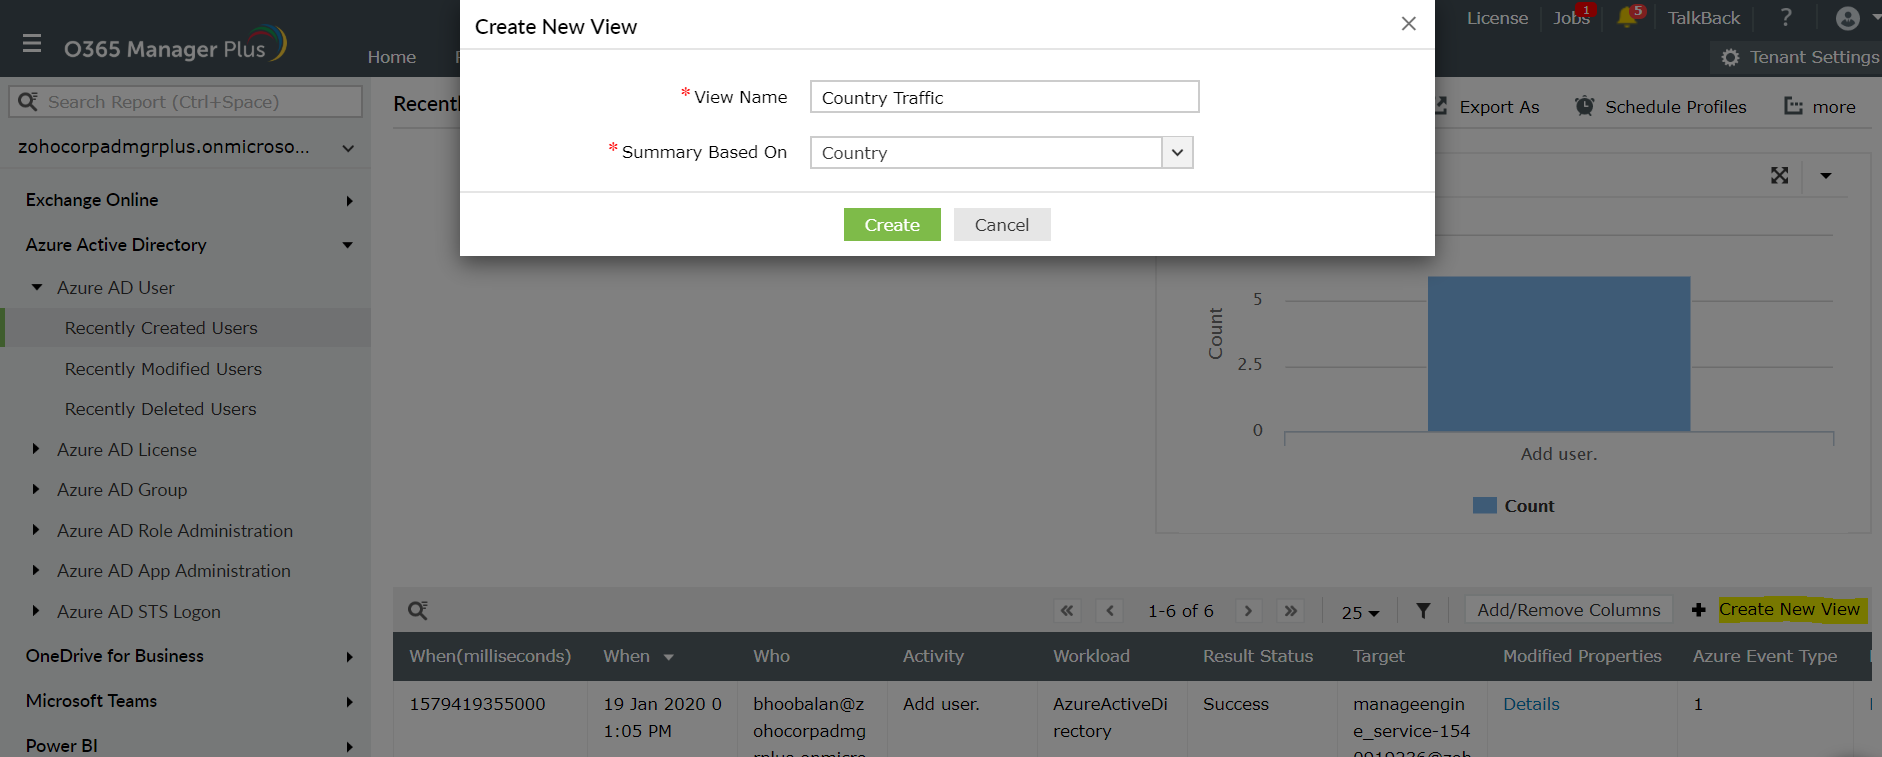
To get a custom view of country-wise traffic, you can use the Create New View option available on the top right corner of the audit reports. Enter a suitable name for the custom report and in Summary Based On section, select Country option.
Sticky Posts
[ManageEngine] Free workshop series on O365 Manager Plus
Hi there, Do you find yourself struggling to manage the different Office 365 services your organization uses with just the native tools? We've got your back! O365 Manager Plus helps you audit, monitor, manage, and report on Exchange Online, Azure AD, and several other Office 365 services. Attend this free workshop series to find out how you can get the most out of O365 Manager Plus. Register now Agenda: Session Title Date & Time AnalyzeO365 Manager Plus User Conference: 2 days of extensive training
Join us for 2 days of learning and fun at our User Conference! During this conference, we will explore ways to help you make the best use of our Office 365 reporting, managing, monitoring, auditing, and alerting solution. You have the option of joining us in Sydney or in Melbourne. <<Learn more and register now>> By attending, you can learn in depth about: Gain real insight into Office 365. Office 365 auditing and compliance management. Office 365 management and help desk delegation made easy.O365 Manager Plus Free Online Webinar - Register Now!
Hello ! How sure are you in securing your Office 365 setup from sophisticated attacks? One sure shot way of defending attacks on your Office 365 platform is to use a solution that provides additional security measures which are not available natively in Office 365. Join us in our next webinar and learn how to cope with the security risks by taking advantage of O365 Manager Plus' features. Topic: Thwart Threats with O365 Manager Plus Date: November 9, 2017 Time: 2 PM EST Presenter: Anupriya[KB] Help Desk Delegation - Create Custom Help Desk Roles
Delegating mundane tasks to help desk technicians or concerned personnel reduces the burden of administrators. With Microsoft's Office 365 administrative console, it is either give access to everything or none. This is not much user-friendly, as you are not allowed to selectively delegate tasks to technicians. A HR personnel should not have access to financial reports. Similarly , front desk technician should not be allowed to add new users. When given full access, the users may knowingly or unknowinglyTrack Microsoft Teams with the all new O365 Manager Plus!
Hello Everybody! We’ve released today a new build of O365 Manager Plus - 4103. The new update supports Microsoft Teams and enhances product’s license management. What’s new? Feature: Microsoft Teams audit and alert : Two audit and alert categories have been added for Microsoft Teams. Microsoft Teams Events: Track events such as channels added, teams created, teams deleted, and users signed in to Teams. Microsoft Teams Settings Changes: Shows the details of channel changes, team changes, and organization