PCI DSS compliance reporting
Hello there!
Your cardholder data environment is constantly evolving and never remains the same.
Firewall rules change. Privileged accounts get modified. New vulnerabilities emerge. Every one of those operational changes quietly shifts your compliance posture.
PCI DSS v4.0 makes this explicit: It demands continuous proof of discipline, not a once-a-year evidence scramble.
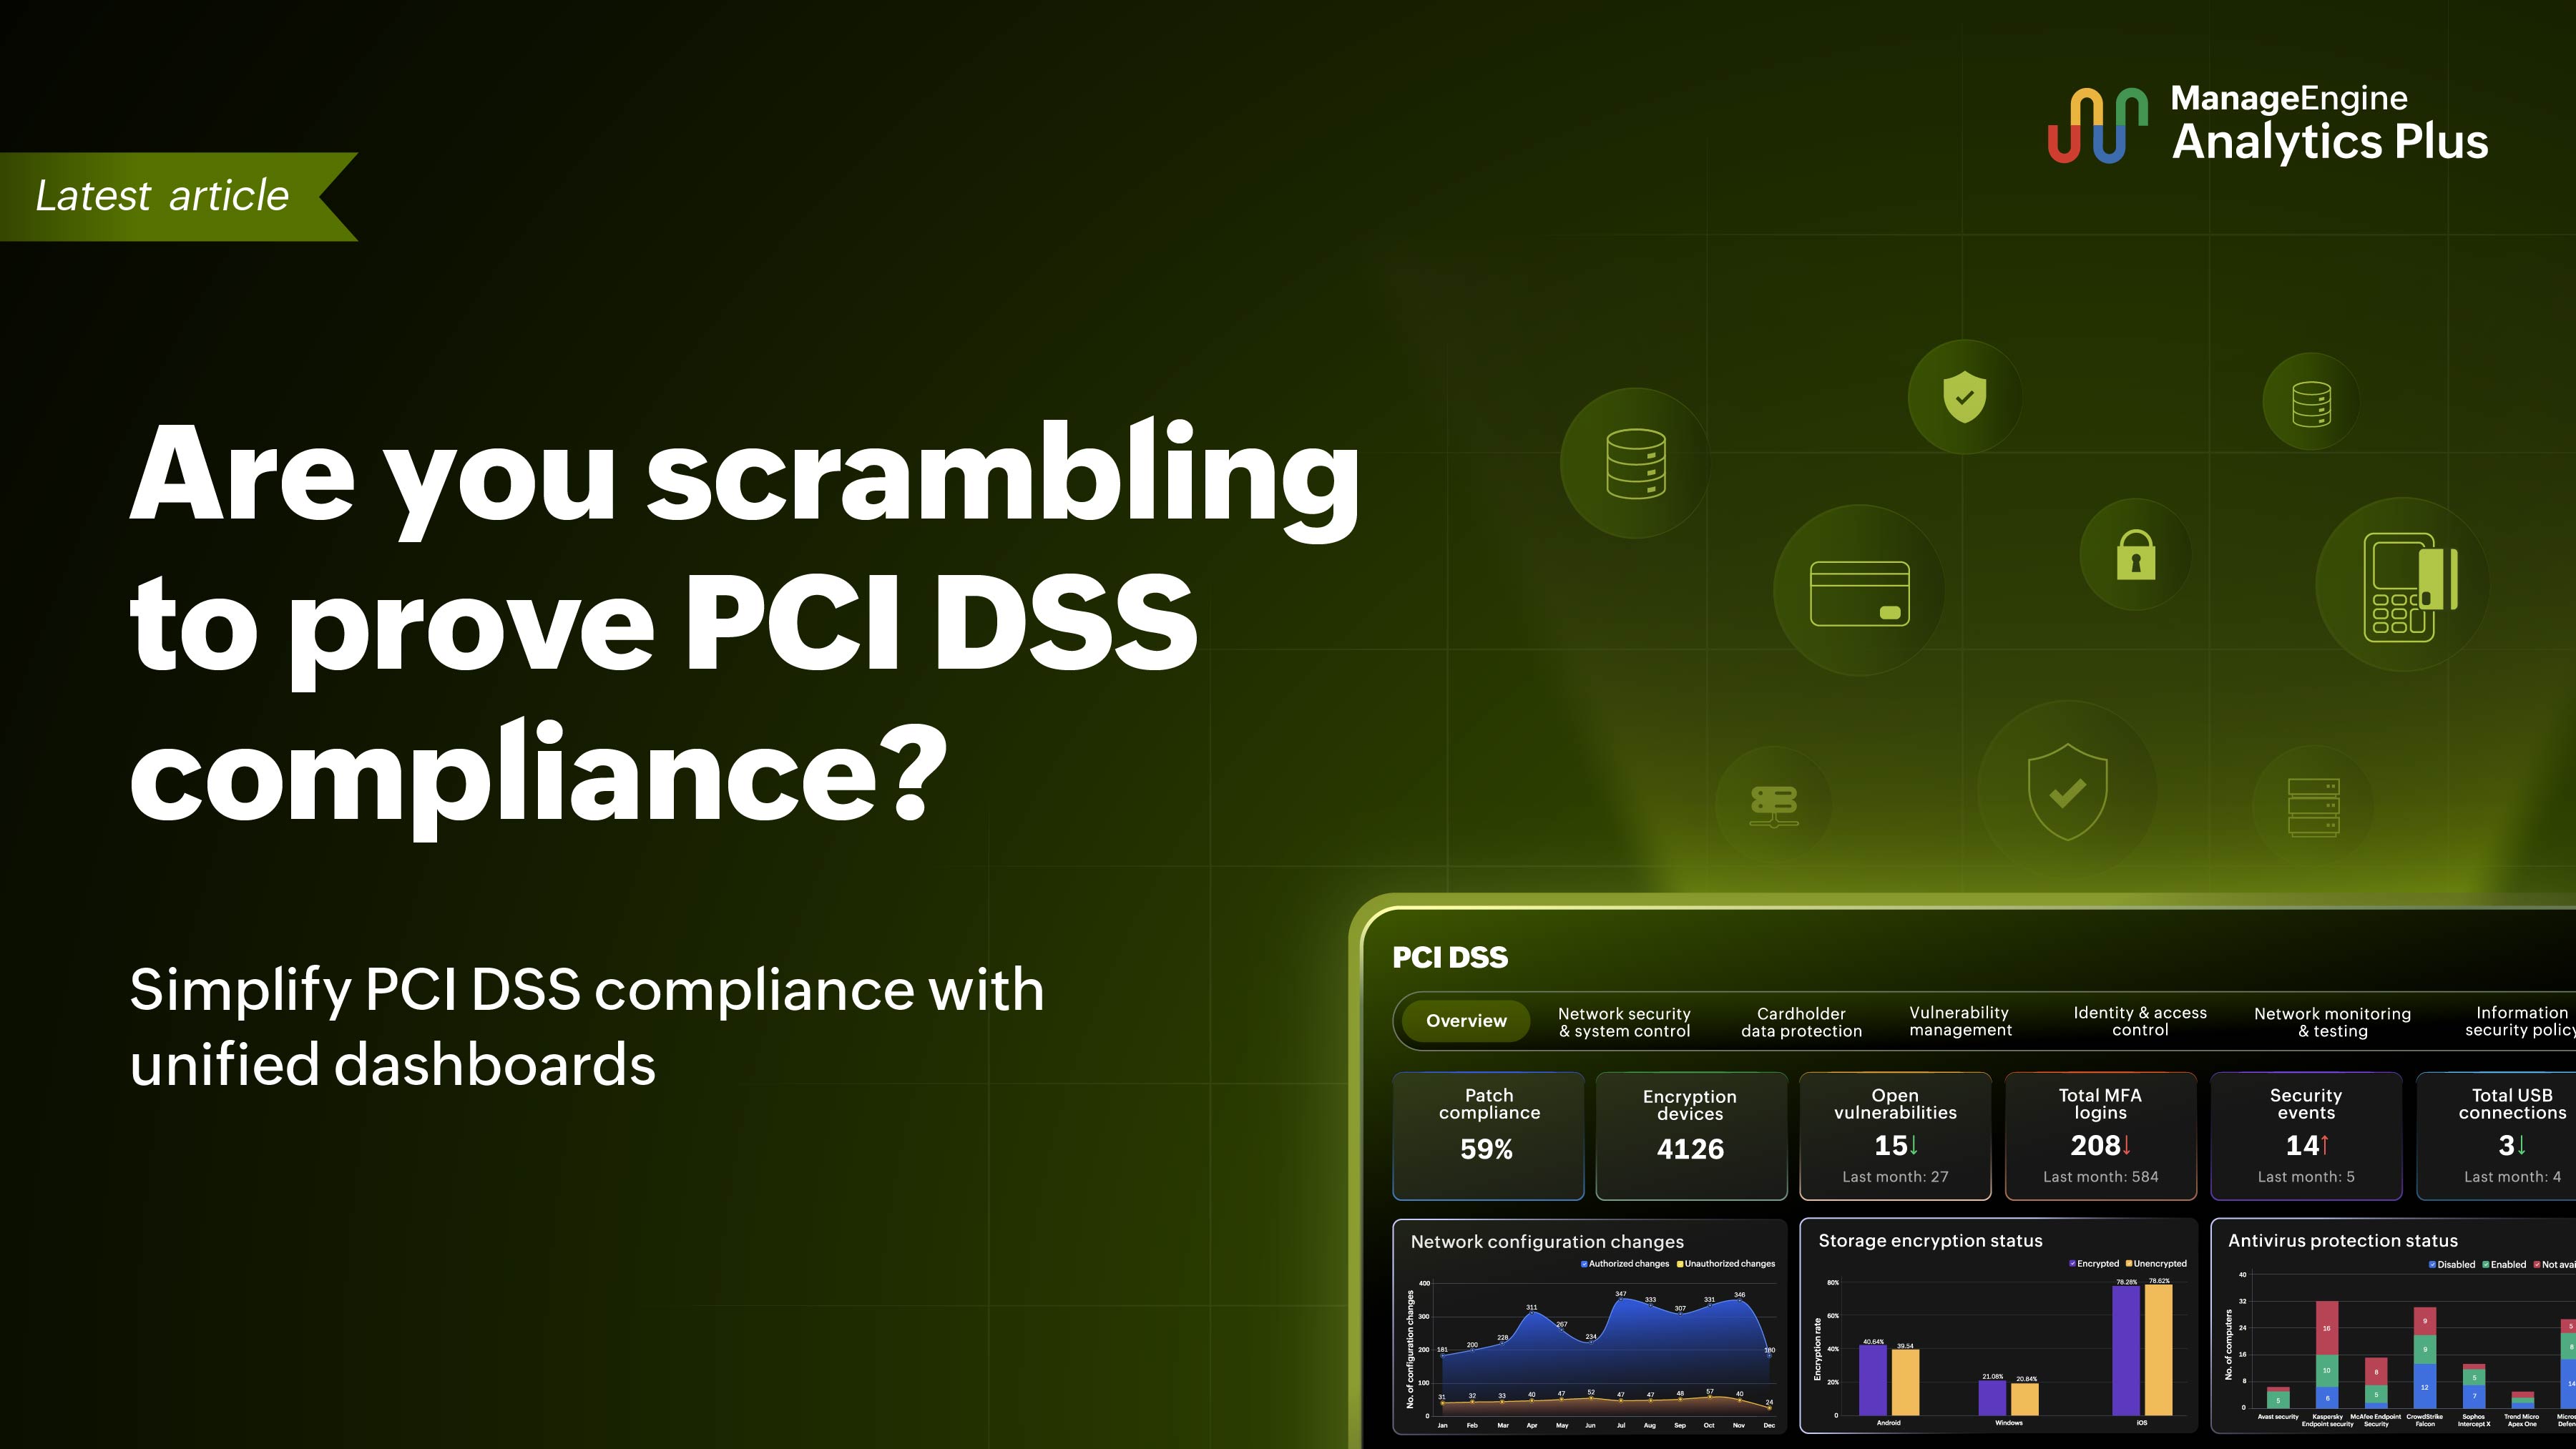
Our latest blog explores how security teams can map telemetry directly to PCI DSS requirements by consolidating firewall activity, ASV scan results, PAN exposure monitoring, MFA authentication logs, privileged account usage, certificate health, and patch compliance into a single, framework-aligned dashboard. The result? Your CDE's compliance posture across all 12 requirements is permanently visible, and not periodically reconstructed.